
Direct Answer
Safeguarding your privacy when using on-device AI agents requires a multi-layered approach: restricting application access, verifying where your data is processed, and keeping human checkpoints in place for high-stakes tasks. While executing tasks directly on local hardware limits cloud exposure, deploying on-device AI agents doesn’t mean your private files are immune to remote data leaks.
Because privacy controls are spread across OS permissions, standalone app toggles, browser extensions, and cloud services, relying on a single settings page is rarely enough.
Understanding On-Device AI Agents and Local Workloads
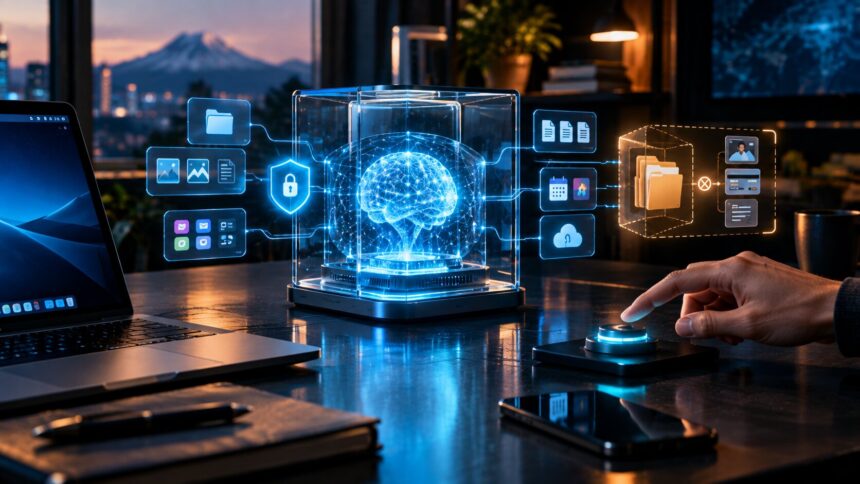
Modern on-device AI agents do far more than process simple text prompts. Depending on how they are configured, these tools can access local directories, re-organize personal files, interact with third-party software, manage calendars, search web pages, and run multi-step automated tasks.
Because many on-device AI agents function as hybrid systems, you need a clear understanding of when information stays on your local machine and when it gets transmitted off-device.
Key Privacy Takeaways
- Limit tool access strictly to the individual folders or files needed for a given task.
- Inspect system-level permissions for sensitive hardware like microphones, cameras, contacts, and location tracking.
- Identify which steps run offline locally versus those requiring external cloud processing.
- Confirm whether your prompts, uploaded files, or chat logs are retained for model training.
- Mandate explicit user sign-off before allowing an agent to send communications, make purchases, or delete files.
- Keep work files separate from personal financial records and sensitive identity documents.
- Share project-specific subdirectories instead of granting broad access to your main drive.
- Disconnect unused app extensions and third-party integrations as soon as you finish a project.
- Recheck your privacy toggles after major software updates, as system defaults can change quietly.
- Maintain activity logs for automated background processes to track actions taken on your device.
How to Audit AI Agent Permissions
Review every connected asset
Start with the AI application itself, then check your operating system security panel. An assistant handling one work folder shouldn’t have unrestricted access to your photo gallery, personal IDs, or root cloud storage drives.
Apply minimal necessary access
A comprehensive privacy check goes beyond basic permissions—it covers data retention policies, model training opt-outs, OS privileges, and active account integrations.
Maintain a routine checkup schedule
Setting a monthly or quarterly reminder helps you catch legacy app connections that were useful once but no longer require access to your device.
Tracking Where Data Processing Happens
Local hardware execution
Processing workloads directly on your device reduces reliance on remote servers, keeping sensitive notes, private voice records, and local docs contained on your physical machine.
Cloud-based infrastructure
Remote cloud engines offer higher computing power, but you must know what information leaves your hardware, how long server logs persist, and whether third-party vendors handle the data.
Hybrid processing setups
Many on-device AI agents combine both approaches. Your security choices should always be governed by the most sensitive data point in your workflow rather than relying on product marketing labels.
To see how major tech companies handle this balance without compromising end-to-end security, you can read more about Apple’s Private Cloud Compute security model.
Enforcing Approval Gates for High-Risk Actions
Manual confirmation is essential before allowing automated tools to execute actions that are difficult to reverse:
- Drafting, sending, or forwarding emails and direct messages
- Authorizing credit card transactions or financial payments
- Deleting, moving, or renaming critical documents
- Sharing private files with external web applications
- Changing security credentials or primary account settings
- Publishing posts or updating live web page
Why Clear Data Boundaries Matter
Restricting system privileges gives on-device AI agents fewer opportunities to interact with files they don’t need. Approval gates keep you firmly in command while routine, low-risk background tasks execute smoothly. Documenting these settings also makes it easier to notice if a software update quietly resets your choices or introduces a new data pipeline.
For broader insights into user data rights and decentralized AI standards, explore Mozilla’s research on trustworthy AI and on-device privacy.
Frequently Asked Questions
Are on-device AI agents always private?
No. While on-device AI agents perform many tasks locally, many still connect to cloud infrastructure, third-party APIs, or external web tools to complete complex requests.
Should an AI agent have access to all files?
No. Grant access only to specific task folders and revoke those privileges once the job is complete.
Can AI agents send emails automatically?
They can, but leaving communication on full autopilot is risky. Sensitive messages should always require a manual preview and explicit confirmation before sending.
Does local AI always run faster?
Not necessarily. Performance depends on your device hardware, system RAM, and model size. Local processing is primarily about data ownership and security, not raw execution speed.
Bottom Line
You can take advantage of on-device AI agents without giving them unrestricted access to your digital life. Set clear permission boundaries, understand where data processing occurs, enforce approval gates, and review connected services regularly to keep your automation secure.
Source: Capgemini TechnoVision Tech Trends. Explore enterprise guidelines on AI agent deployment, security, and governance on the official Capgemini Research Library.
Related reading on techharvey.com: Data Risks and Keeping Information Secure; How AI-Driven Technology Is Shaping Services.